Filtered by tag: data breach × Clear

Cybercriminals Are Selling Corporate Executives’ Social Security Numbers for Just 25 Cents
Matched: health
Rapid7 has tracked 476 compromised SSN records tied to 395 corporate executives on dark web marketplaces since early 2026, with records selling for as little as 25 cents. C-suite executives account for 44.6% of affected profiles. Three platforms — Xilo, Bankomat, and PeopleFinder — represent 81.5% of leaks, sourcing data from large breaches, infostealers, and phishing. Unlike passwords or cards, SSNs cannot be changed, making them permanently exploitable for fraud and impersonation schemes.
Boston Scientific says cyberattack is causing a ‘global disruption’ to medical device operations
Matched: medical
Boston Scientific confirmed a cyberattack causing global disruptions to IT systems and operations, filing an 8-K with the SEC. The incident has impacted order processing and shipping, with third-party cybersecurity experts brought in to assist. The attack type was not disclosed, though the disruption pattern suggests ransomware. No group has claimed responsibility, and no stolen data has been reported. Full restoration timeline remains unknown.
Healthtech firm CareCloud reveals March 2026 data breach impacted 3.7 million patients
Matched: health
Healthcare technology company CareCloud has disclosed a data breach from March 2026 that affected approximately 3.7 million patients. The company is notifying those impacted, though it has not revealed what specific types of patient information were compromised in the incident.
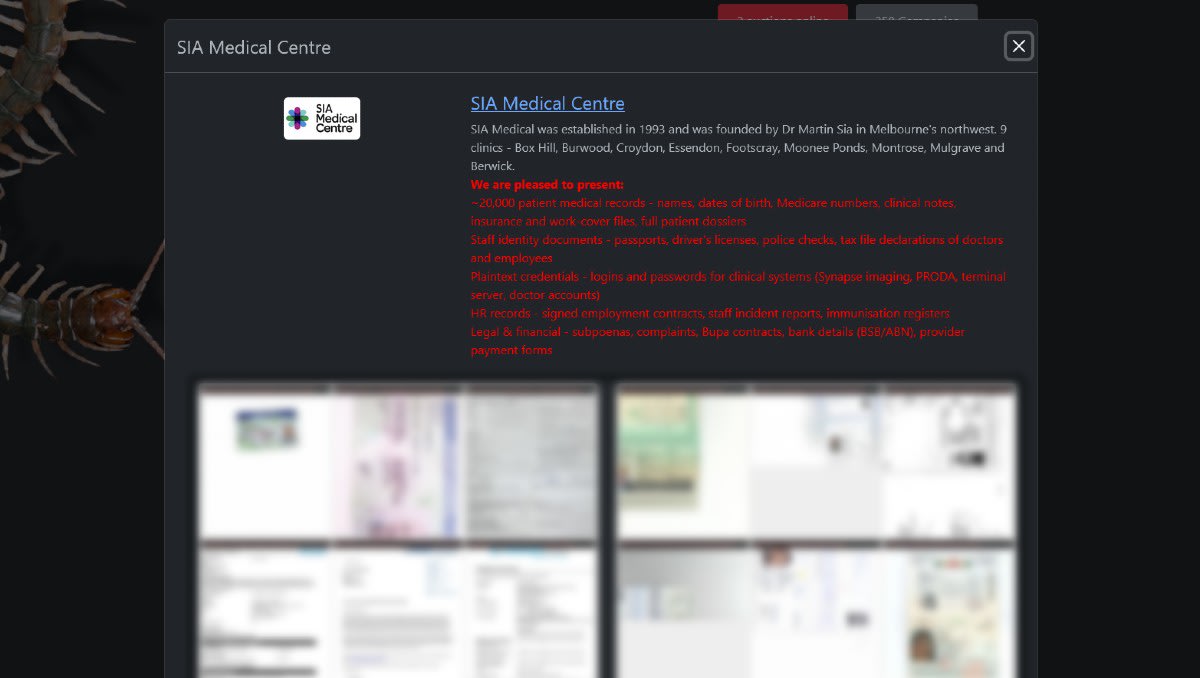
Exclusive: SIA Medical Centre confirms it is investigating cyber incident involving patient data
Matched: medical
Victorian medical centre SIA Medical Centre is investigating a ransomware attack after the Rhysida cyber extortion group claimed to have obtained thousands of patient records. The centre confirmed it is responding to a cyber incident involving patient data. Rhysida, a known ransomware group, has listed the stolen data and is threatening to release it unless a ransom is paid.
Exclusive: Kairos ransomware lists Warwick Fabrics NZ as hack victim
Matched: medical
New Zealand textile company Warwick Fabrics has been listed as a victim by the Kairos ransomware group, which claims to have stolen 386 gigabytes of data. The alleged breach includes sensitive employee information such as passports, medical reports, and salary data. The company has not yet publicly responded to the claims.
Updoc says a cyber incident may have exposed customer data
Matched: health
Australian telehealth provider Updoc has disclosed a cybersecurity incident that may have exposed customers' personal data. The company said it became aware of the breach and is investigating the extent of unauthorized access. Updoc offers 24/7 telehealth services and holds sensitive patient information, raising concerns about the nature of the data potentially accessed by threat actors.
Exclusive: Partnered Health responds to Inc Ransom data breach claims
Matched: health
Australian GP network Partnered Health is responding to claims by cyber extortion group Inc Ransom, which alleges it stole terabytes of data from the organisation. At least 21 clinics may be affected. Partnered Health has not confirmed the breach's extent. Inc Ransom typically publishes stolen data if ransoms go unpaid, raising concerns about potential exposure of sensitive patient information.

Partnered Health confirms cyber incident affecting patient information across national clinic network
Matched: health
Partnered Health has confirmed a cybersecurity incident in which unauthorised parties accessed patient data across its national clinic network. The breach affected personal and health information held by some clinics. The company is investigating the extent of the incident and has notified relevant authorities. Affected patients are being contacted and advised to monitor for suspicious activity.